Lab 1-1
Using PowerShell's Get-FileHash cmdlet and searching VirusTotal using the resulting hashes reveals that both files are considered malicious by the majority of vendors.
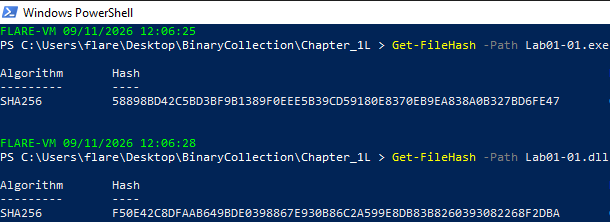
Figure 1: SHA256 hashes for Lab01-01.exe and Lab01-01.dll.
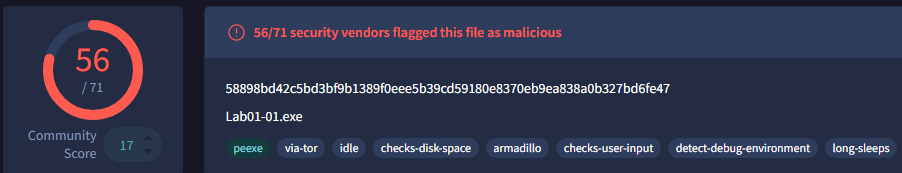
Figure 2: VirusTotal results for Lab01-01.exe.
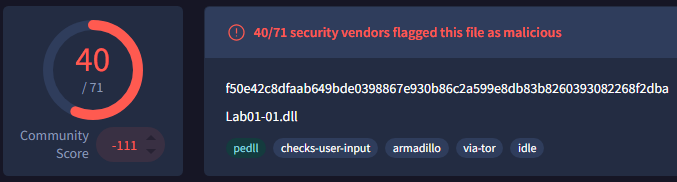
Figure 3: VirusTotal results for Lab01-01.dll.
Looking at the IMAGE_FILE_HEADER section of the Lab01-01.exe shows the compilation TimeDateStamp as 2010-12-19 08:16:19. The TimeDateStamp of Lab01-01.dll shows that it was compiled 19 seconds after the Lab01-01.exe file (2010-12-19 08:16:38).
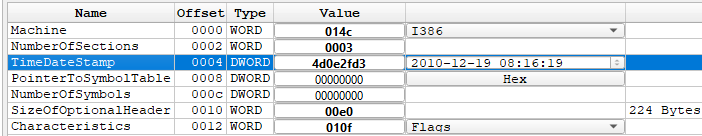
Figure 4: The Lab01-01.exe IMAGE_FILE_HEADER values shown in Detect It Easy.
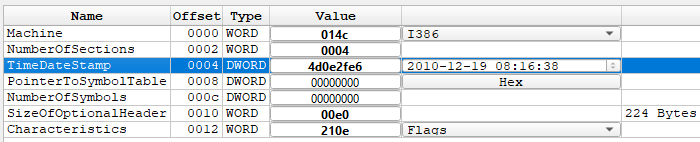
Figure 5: The Lab01-01.dll IMAGE_FILE_HEADER values shown in Detect It Easy.
The Detect It Easy Automatic scan doesn't indicate that either file is packed. Looking at the .text section for Lab01-01.exe shows the VirtualSize and SizeOfRawData to be roughly equal in size, suggesting the file is not packed. There are also plenty of visible entries under the Strings tab suggesting the file hasn't been obfuscated.
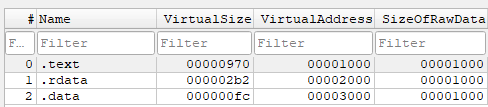
Figure 6: The Lab01-01.exe PE sections.
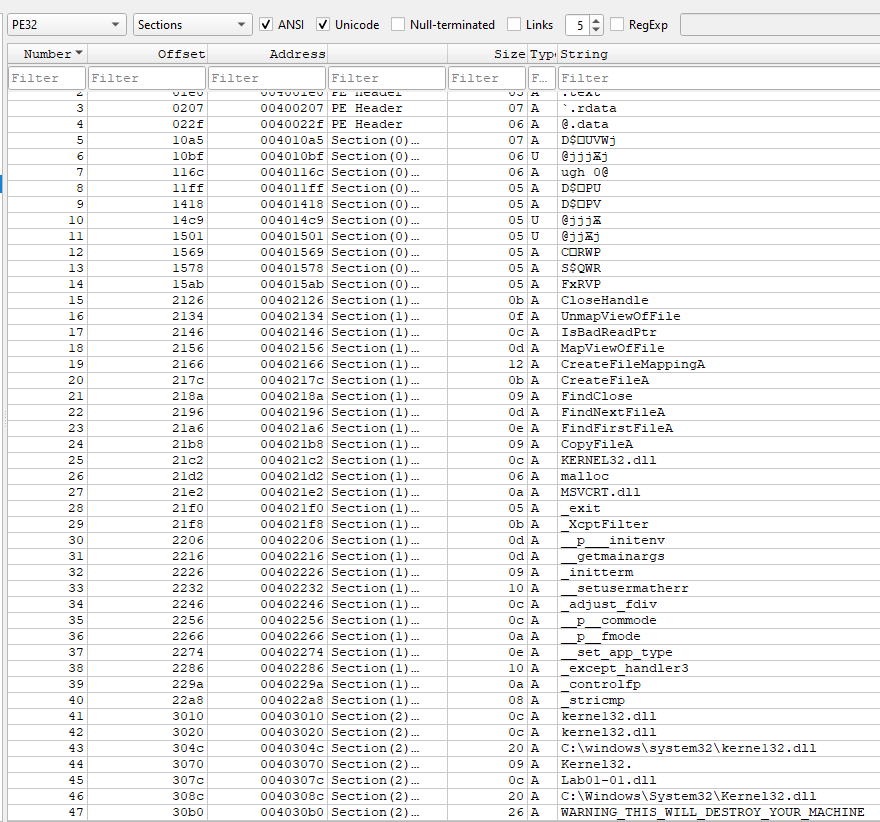
Figure 7: The Lab01-01.exe Strings tab.
Conducting the same checks on the Lab01-01.dll file shows the .text section having a smaller VirtualSize than SizeOfRawData but it doesn't appear to be packed. The Strings tab also has lots of entries which indicates it is not obfuscated.
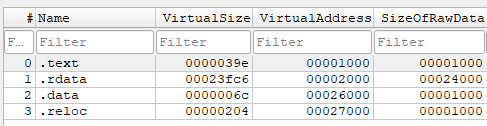
Figure 8: The Lab01-01.dll PE sections.
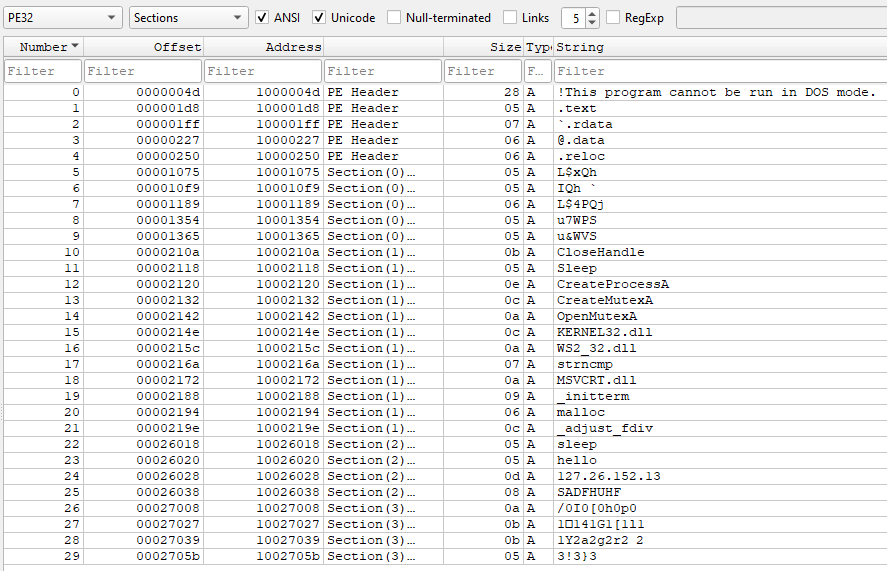
Figure 9: The Lab01-01.dll Strings tab.
Looking at the imports for Lab01-01.exe, we can see CreateFileA, FindFirstFileA, FindNextFileA, CopyFileA and others being imported. This indicates that the program is searching for and manipulating files on the system.
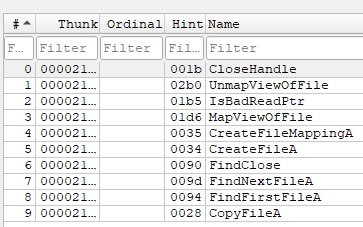
Figure 10: Lab01-01.exe's KERNEL32.dll import list.
The KERNEL32.dll imports for Lab01-01.dll show CreateProcessA, Sleep, and CreateMutexA. There is also the presence of WS2_32.dll which is used for network communication. The functions are imported using their ordinal values so I mapped them to their english values.
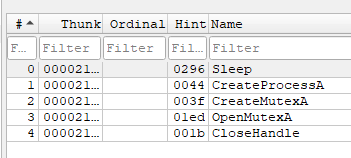
Figure 11: Lab01-01.dll's KERNEL32.dll import list.
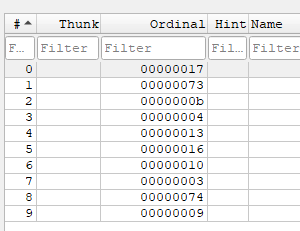
Figure 12: Lab01-01.dll's WS2_32.dll ordinal values.
These values map out to:
- 17 =
imp_recvfrom - 73 =
imp_WSAInstallServiceClassW - 0b =
imp_inet_addr - 04 =
imp_connect - 13 =
imp_listen - 16 =
imp_recv - 10 =
imp_ioctlsocket - 03 =
imp_closesocket - 74 =
imp_WSARemoveServiceClass - 09 =
imp_htons
It appears that the .dll contains code that will be used to launch external web requests and listen for a response.
Host-Based Indicators
The Lab01-01.exe .data section shows the strings C:\Windows\System32\Kernel32.dll and C:\windows\system32\kerne132.dll. We know that it also is importing file manipulation functions so we can take an educate guess that it is replacing KERNEL32.dll with KERNE132.dll.
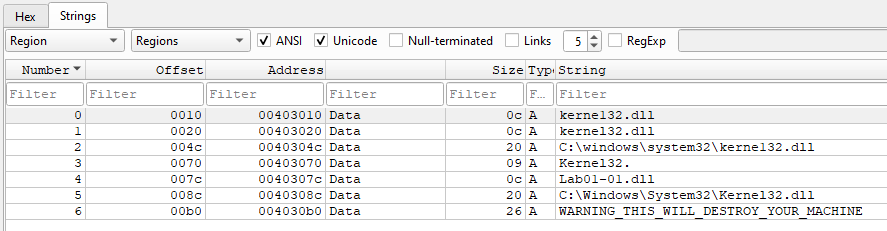
Figure 13: Lab01-01.exe's strings found in the .data section of the PE.
Network-Based Indicators
The Lab01-01.dll's .data section shows the ip requests will be made to: 127[.]26[.]152[.]13.
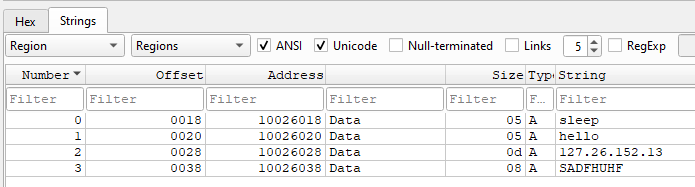
Figure 14: Lab01-01.dll's .data section strings.