About This Game
Afomiya Storm is a rising social media influencer who just landed a new role at CloutHaus. A fake collaboration email slips into her inbox, and one click gives an attacker access to her account. Hidden rules, strange filters, and rerouted emails follow.
Your job is to trace the phishing attack, uncover how the intruder got in, and stop it before it spreads.
Why This Module
Phishing is the #1 alert type handled by SOC T1 analysts. This module walks through a realistic social-media-enabled phishing scenario, teaching analysts how to identify malicious email content, trace attack chains, and spot identity abuse — all typical T1 escalation triggers.
Learning Objectives
- Identify phishing and spear-phishing tactics
- Recognize and analyze social engineering techniques
- Investigate malicious email forwarding rules and inbox filters
- Use KQL to investigate security incidents
- Learn the impact of MFA - and what happens when it’s missing
- Understand how oversharing and public data fuel targeted attacks
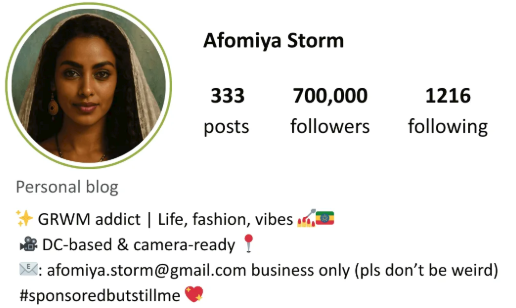
Figure 1: Afomiya's Instagram profile.
Based on Afomiya's Instagram profile, what is the email address she uses for brand deals?
afomiya.storm@gmail.com is listed as her business email.
Which of the following signs should Afomiya look for to determine if an email offering a brand deal is a phishing attempt?
A. The email contains urgent or threatening language, pressuring her to act quickly, such as "Immediate action required" or "Deadline in 24 hours."
B. The email asks for sensitive information like her password, credit card details, or social security number.
C. The email comes from a domain name that looks suspicious or doesn't match the legitimate brand's official domain.
D. The email has generic greetings like "Dear Customer" instead of addressing her by name or title.
E. All of the above. ✅
What technique is the threat actor using to manipulate her into revealing personal information that could compromise her email or Instagram account?
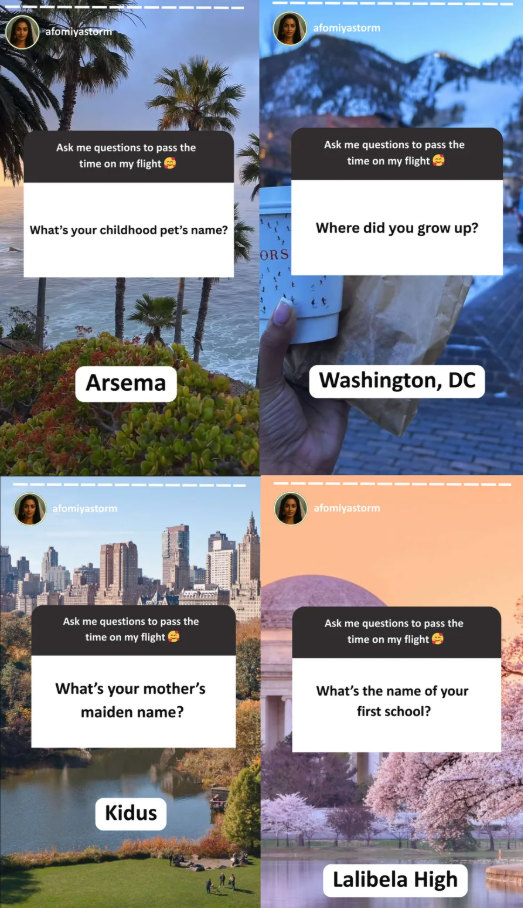
Figure 2: The attacker using social engineering to learn her account recovery answers.
The attacker used social engineering to discover her account recovery answers.
What answers did the attacker entry to try and bypass the security questions?

Figure 3: The attacker's GET request in the authentication log.
Question 1: What's the name of your first school?
Answer: Lalibela
Question 2: What's your mother's maiden name?
Answer: Kidus
According to CloutHaus internal employee logs, what is Afomiya's designated professional email?
Using the query below and reading the results shows her new professional email as: afomiya_storm@clouthaus.com.
Employees
 | where name contains "afomiya"
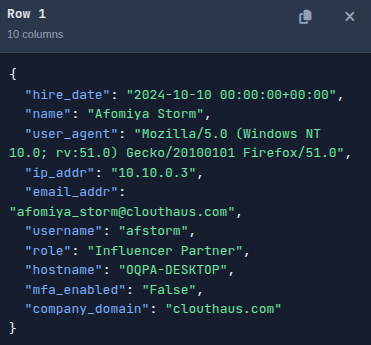
Figure 4: KQL query results showing Afomiya's information.
Based on the CloutHaus employee table, what is the status of Multi-Factor Authentication (MFA) for Afomiya's account?
Employees
 | where name contains "afomiya"
 | distinct mfa_enabled
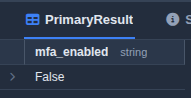
Figure 5: mfa_enabled value of False.
Her CloutHaus account does not have MFA enabled.
What is the sender's email address in the email Afomiya received from "Dior"?
Email
 | where recipient == "afomiya_storm@clouthaus.com"
 | where subject contains "Dior"
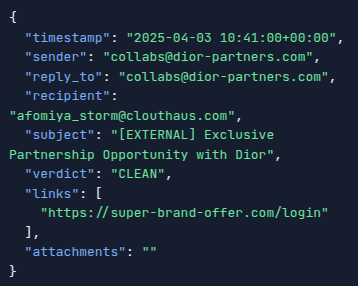
Figure 6: External email information.
collabs@dior-partners.com
What is the subject line of the email Afomiya received from "Dior"?
[EXTERNAL] Exclusive Partnership Opportunity with Dior
What is the link provided in the email?
https://super-brand-offer.com/login
When did Afomiya click on the link?
OutboundNetworkEvents
 | where url contains "https://super-brand-offer.com/login"
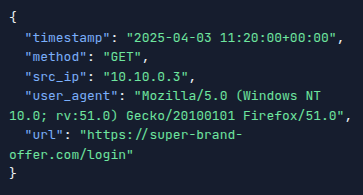
Figure 7: Outbound GET request showing when Afomiya clicked the link.
The timestamp key shows the value 2025-04-03 11:20:00+00:00.
What username did she enter?
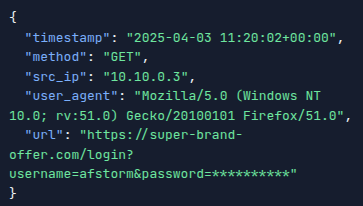
Figure 8: Credentials entered into the attacker's cloned page.
afstorm
What is the IP address associated with the domain?
Using the PassiveDNS table we can check domain information with the following query.
PassiveDNS
 | where domain == "super-brand-offer.com"
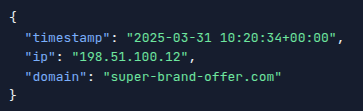
Figure 9: The IP address associated with the domain.
198.51.100.12
How many distinct domains are linked to the suspicious IP address?
We can find this by selecting distinct domains belonging to the IP we found.
PassiveDNS
| where ip == "198.51.100.12"
| distinct domain
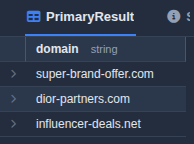
Figure 10: Distinct domains found for the 198.51.100.12 IP address.
There are 3 distinct domains found for 198.51.100.12 in the PassiveDNS table.
Based on the images showing the apartment view and amenities from Afomiya's Instagram post, use a reverse image search to identify the name of the apartment building.
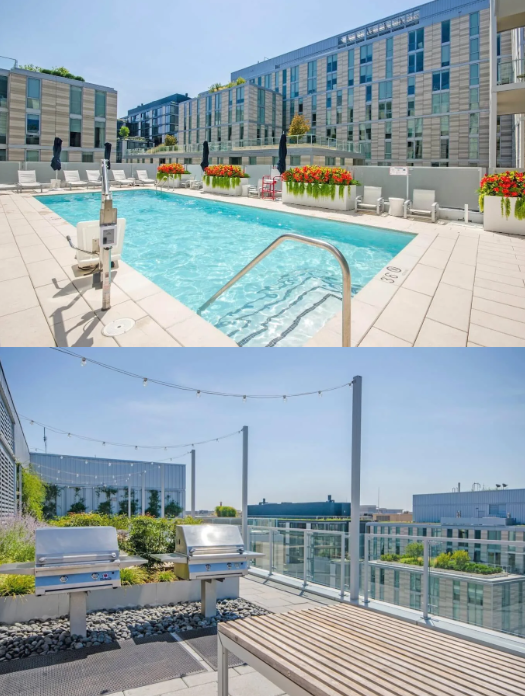
Figure 11: Afomiya's Instagram post.
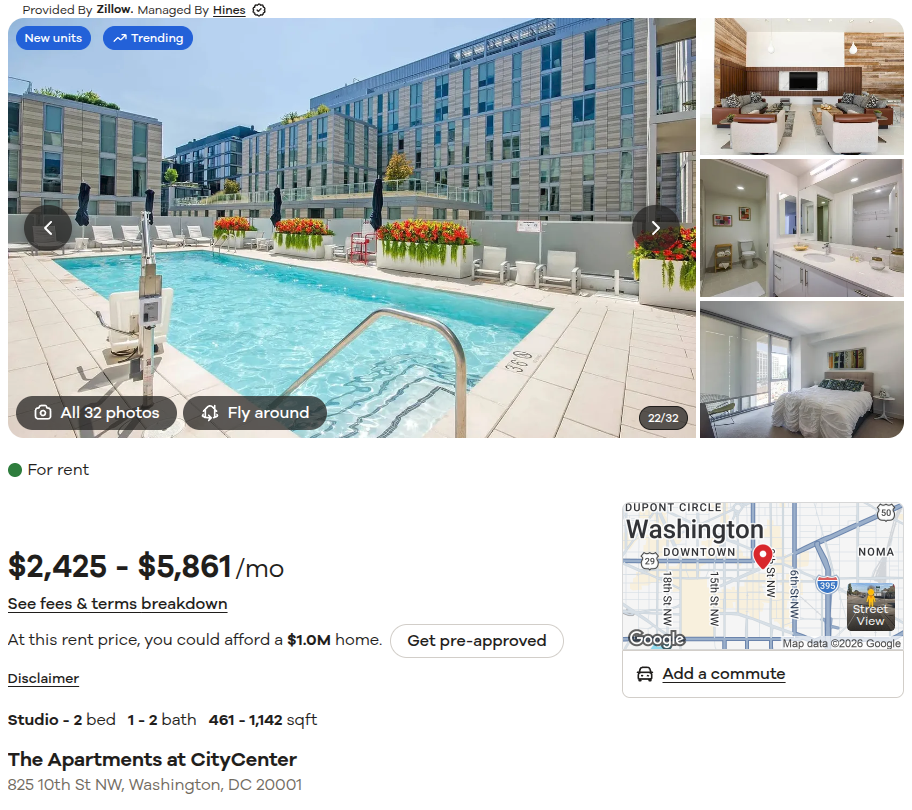
Figure 12: Location found using Google's reverse image search.
The Apartments at CityCenter